
Semgrep
Rule based static analysis with AI triage for code, supply chain and secrets scanning.
Best for Security teams writing custom SAST rules
Used Semgrep and liked it? Upvote it. One upvote per person. Upvotes come from visitors, not from us, and never change "Our ranking".
What it does
Semgrep is an application security platform that brings together static code analysis, software composition analysis, and secrets detection. You connect your repositories or run scans in your continuous integration workflows and developer tools to receive contextual findings, automated triage, and step by step remediation. It is designed for developers, application security teams, and CISOs who want to fix real code vulnerabilities before shipping.
Read more: 5 features and how people use themShow less
-
Semgrep Code static analysis
Scans first party code using rules, data flow analysis, and cross file analysis to identify security issues like cross site scripting and SQL injection. It surfaces code findings directly inside developer workflows such as continuous integration and pull request comments.
Use caseA developer runs checks on a pull request before merging to detect and resolve an injection vulnerability right within the existing review process.
From docs.semgrep.dev/semgrep-code/overview -
Custom rules engine
Provides an open rule system where teams write custom rules using transparent syntax and pattern matching. It lets you inspect how issues are detected and customize rule messages delivered to developers.
Use caseA security engineer drafts custom rules to enforce internal company secure coding guidelines across all private repositories.
From docs.semgrep.dev/semgrep-code/overview -
Semgrep Supply Chain reachability analysis
Inspects open source dependencies and compares vulnerable library definitions against your actual codebase. It distinguishes between reachable and unreachable vulnerabilities so teams can prioritize packages that are genuinely exposed.
Use caseAn AppSec team audits open source dependencies during a deployment build and skips alerts for imported libraries whose vulnerable functions are never called.
From docs.semgrep.dev -
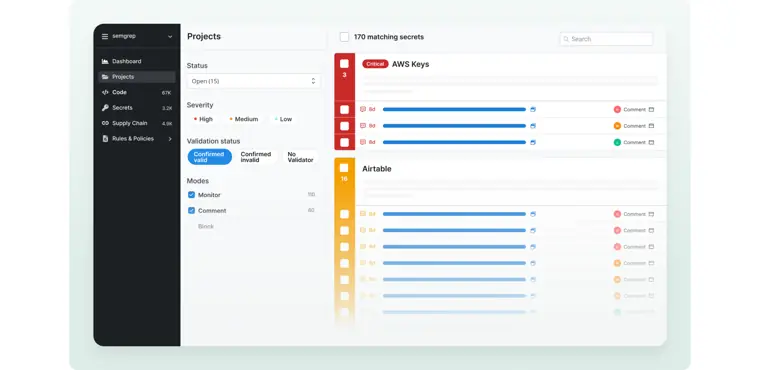
Secrets detection
Finds exposed credentials and sensitive tokens across code using semantic analysis, entropy calculations, and secret validation. It blocks leaked credentials before commit or identifies existing exposures via historical repository scans.
Use caseA software engineer connects a pre commit hook to verify that no live API keys or access tokens are committed to source control.
From semgrep.dev/pricing · image from Semgrep -
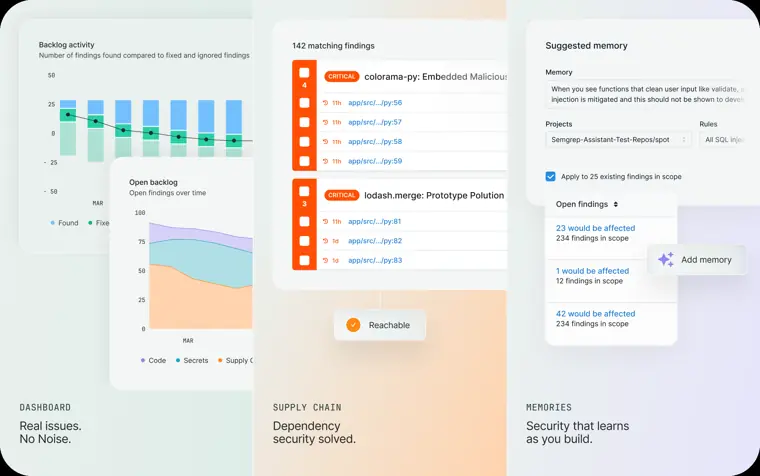
AI triage and remediation
Analyzes surrounding code context and developer intent to provisionally ignore false positives and produce concrete code fixes. It remembers triage choices to automatically suppress identical findings in the future.
Use caseA developer reviews a pull request comment containing AI generated guidance to fix a complex authorization flaw without manually researching remediation patterns.
From semgrep.dev · image from Semgrep
Written from Semgrep's own website, checked . Each feature links to the page it comes from; images are Semgrep's own.
Every plan
| Plan | Monthly | Billed yearly | Per | What it includes |
|---|---|---|---|---|
| Free | Free | Not listed | per contributor | up to 10 contributors, 10 private repos, 60 AI credits |
| Teams (Code / Supply Chain) | $30 | Not listed | per contributor, per product | 500 private repos, 20 AI credits/dev/month |
| Teams (Secrets) | $15 | Not listed | per contributor | secrets scanning add on |
| Enterprise | Contact sales | Not listed | custom | contact sales; unlimited repos, 50 AI credits/dev/month, on prem SCM, dedicated infra |
From Semgrep's own pricing page, checked . Prices are in US dollars per month; "billed yearly" is the monthly price when you pay for a year up front. A few figures (often the yearly price) are derived rather than printed on the page.
Before you pay
- Unused credits roll over
- Partial
What Semgrep says
Entitlement credits, or the credits that come with your Semgrep licenses, expire at the end of your contract and do not roll over. Credits that you purchase expire at the end of your contract, but they can be rolled over once to the following year.
Source page - Trains on your data
- No
What Semgrep says
Model vendors are not allowed to use the submitted code for training their models.
Source page - Discounts
- Startup discounts available upon application.
What Semgrep says
Small teams may be eligible for Semgrep’s discounted startup pricing. Fill out the form to apply.
Source page - Support
- Community, email, account manager
What Semgrep says
Support Type Community based Award Winning Support Award Winning Support, Dedicated account manager
Source page
Only what Semgrep's own pages state, with the quote behind each answer. Anything they don't publish is left out rather than guessed.
Getting started with Semgrep
- Install the Semgrep CLI using pipx, uv, or Homebrew.
- Log in to your Semgrep account via the CLI by running semgrep login and activating it in your browser.
- Turn on cross file analysis under Settings > General > Code in the Semgrep AppSec Platform.
- Navigate to the root of your codebase and run your first scan using semgrep ci or semgrep scan.
Written from Semgrep's own help pages: docs.semgrep.dev/getting-started/cli
What the free plan includes
Up to 10 contributors, 10 private repos, 60 AI credits
Questions people ask about Semgrep
How much does Semgrep cost?
Paid plans start at $15 a month (Teams (Secrets)). 4 plans are listed above, from Semgrep's own pricing page.
Is Semgrep free?
Yes, there is a free plan: Up to 10 contributors, 10 private repos, 60 AI credits.
Do unused Semgrep credits roll over?
Partly: some unused credits carry over, with limits. Source
Does Semgrep train its AI on my data?
No, the company says your data is not used for training. Source
Does Semgrep have a student or other discount?
Startup discounts available upon application. Source
Does Semgrep have an API?
Yes.
How are contributors counted?
A contributor is someone who made at least one commit to your organization's private repository scanned by Semgrep in the past 90 days. Source
Is there special pricing for early stage startups?
Yes, Semgrep offers special pricing for startups upon contacting them. Source
Is private source code shared with Semgrep?
No, if run locally or in CI, source code does not leave your environment; only metadata is sent, and AI processing restricts vendor training. Source
What happens if an organization exceeds its contributor limits on a free license?
Semgrep automatically starts a free trial of the Teams plan the first time limits are exceeded. Source
Works with
- Integrations
- VS Code, JetBrains, GitHub, GitLab, Bitbucket, Azure, Jira, Slack, Cursor, Replit
- AI models
- OpenAI, Amazon Bedrock
- Languages
- 35+ languages
Where this came from
Plans, prices and limits were copied from Semgrep's own pages and the other sources listed, then checked .
- semgrep.dev/pricing
- docs.semgrep.dev/getting-started/scm-support
- docs.semgrep.dev/compliance/soc2
- semgrep.dev/
- semgrep.dev/pricing/
- docs.semgrep.dev/usage-and-billing/overview
- docs.semgrep.dev/semgrep-supply-chain/license-compliance
- docs.semgrep.dev/getting-started/cli
- semgrep.dev/legal/privacy/
- docs.semgrep.dev/semgrep-code/ai-powered-detection-concepts
- docs.semgrep.dev/semgrep-guardian/overview
How we collect prices and rank tools · Is something wrong? Correct this listing
Others that do the same job
 Aikido Securityaikido.dev
All in one AppSec platform: SAST, dependency, secrets, container, cloud scanning plus runtime protection and pentests.
- Green flag: Free plan
- Green flag: No card for trial
 Snyksnyk.io
Developer security platform scanning code, open source dependencies, containers and IaC with AI assisted fixes.
- Green flag: Free plan
- Green flag: No card for trial
 Shopifyshopify.com
Leading ecommerce platform with Sidekick AI that designs stores, writes product copy and edits photos.
 Squarespacesquarespace.com
Design led website builder with AI site generation, built in commerce, scheduling and AI visibility tracking.
- Green flag: No card for trial
- Red flag: Credits reset monthly
 Dorikdorik.com
No code AI website builder with CMS, blogging, white label client dashboard and lifetime plans.
 FlutterFlowflutterflow.io
Visual low code builder for Flutter mobile, web and desktop apps with AI generation and code export.
- Green flag: Free plan
- Red flag: Free plan watermark